Skip to content
Securosophy
Information Security blog that lost it on the way
Menu
About this blog
$whoami
Dating as a form of Penetration Testing
“Know thy Linux” – The Satori Suite
Teaching an Old Dog (not that new) Tricks. Stego in TCP/IP made easy (part-1)
Pozzo & Lucky, The phantom Shell. Stego in TCP/IP (part-2)
Pozzo & Lucky Busted. The Tales of a Mathematician / SOC analyst… (Part-3)
How compliance kills Security (and Romance)…
Trust: a tale of Security, Philosophy, Reverse Engineering and Python
Information Gathering is not enough. Meet GatherOS …
In the Twisted mind of Upper Management
A Git Tutorial of Human Psychology
Reinventing the Wheel for the last time. The “covertutils” package.
Between an Incident Response and a Break-up
The Hassle Exploit
Thoughts on an “Obsessive Simulation of a Critical Procedure”
Kubernetes – a psycho-political view
Red Team Ops Psychology – an Act in 4 Parts
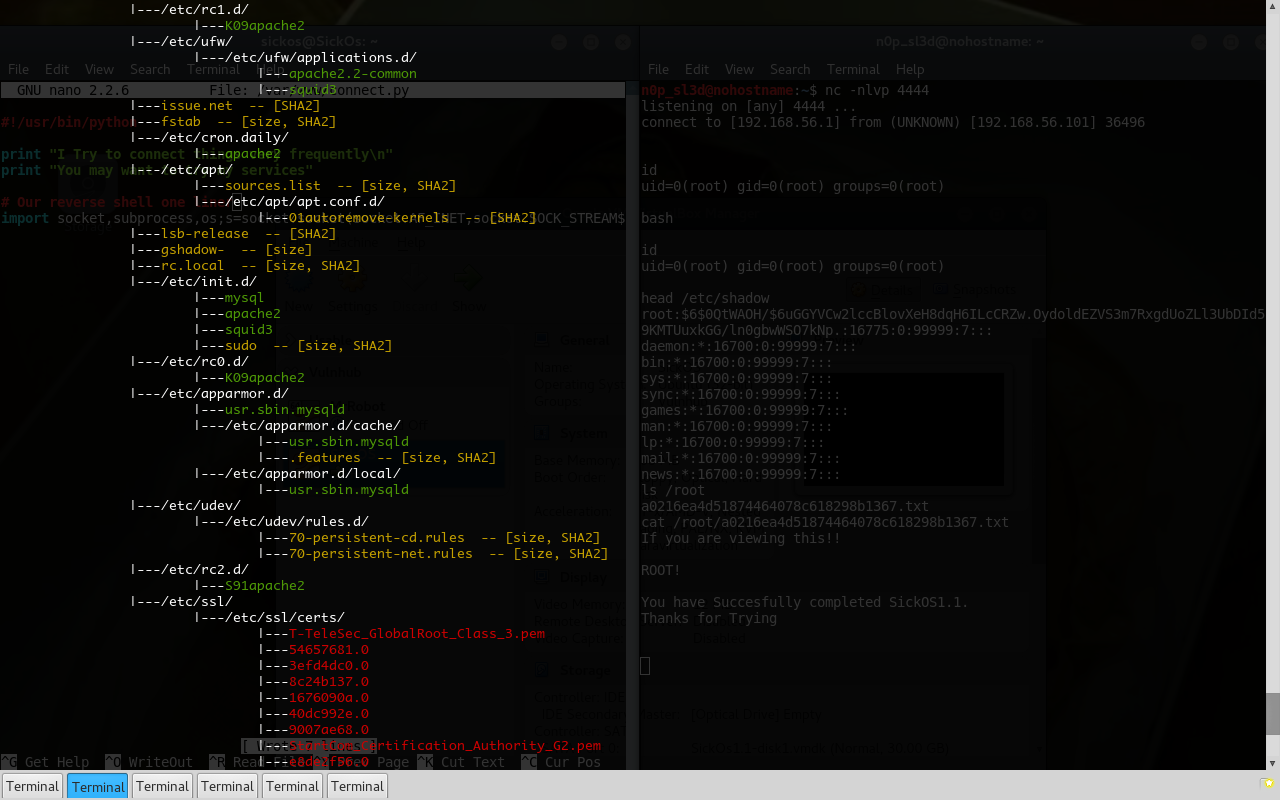
Screenshot from 2016-08-14 22-18-44
Post navigation
“Know thy Linux” – The Satori Suite
Privacy & Cookies: This site uses cookies. By continuing to use this website, you agree to their use.
To find out more, including how to control cookies, see here:
Cookie Policy
Subscribe
Subscribed
Securosophy
Sign me up
Have a WordPress.com account?
Log in now.
Securosophy
Copy shortlink
View post in Reader
Manage subscriptions
Sign up
Log in
Report this content
Collapse this bar
Create your own website, free on WordPress.com.
Create your own website.
Start free